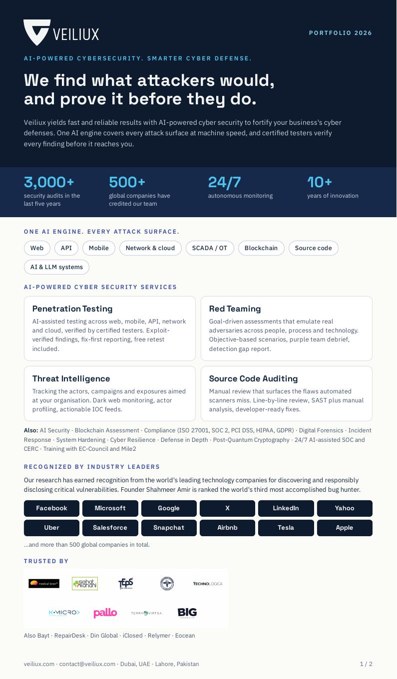
Veiliux 2026 Portfolio Report
Explore the engagements, clients and outcomes behind our year.
Download PDFResources
The full detail behind every Veiliux service, training track, industry and deployment , organised so you can find the answer without a sales call.
Explore the engagements, clients and outcomes behind our year.
Download PDFA detailed reference for every Veiliux service: what is covered, how the engagement runs, and what you receive at the end.
A penetration test measures how an attacker would actually reach your data, then proves each path with a controlled exploit.
A Veiliux penetration test is an adversary simulation rather than a compliance checkbox. We begin by mapping the estate the way an attacker would see it: internet-facing applications, forgotten staging hosts, exposed APIs, third-party integrations, cloud storage, remote access points and the identities that tie them together. AI-assisted reconnaissance compresses days of enumeration into hours and shortlists the paths most likely to succeed, but every candidate finding is confirmed by a certified tester before it reaches your report.
Testing itself is chained rather than isolated. A medium-severity information disclosure is only interesting when it unlocks an authentication bypass, which in turn exposes an administrative function that reaches the database. We document those chains explicitly, because the realistic risk of an environment is almost never the sum of its individual issues. Where safe to do so, exploitation is carried through to proof, with screenshots, request and response pairs, and reproduction steps that your engineers can replay in a lab.
Reporting is written for two audiences in one document. An executive section states, in plain language, what an attacker could achieve, what it would cost the business and which three actions reduce most of that risk. A technical section gives per-finding detail: affected assets, CVSS and exploitability rating, evidence, remediation guidance specific to your stack, and references. After you remediate, a retest is included: we re-run the relevant test cases and reissue the report with the closed items marked, which is usually the artefact your customers or auditors want to see.
How long does a penetration test take?
Most web or network engagements run five to fifteen testing days depending on application count, user roles and environment complexity.
Will testing disrupt production?
Destructive techniques are excluded by default and high-risk actions are agreed in advance. Load-sensitive systems are tested in windows you choose.
A red team assessment tests your entire defence, not a list of assets, by pursuing a real objective the way an adversary would.
A penetration test asks whether your systems have weaknesses. A red team assessment asks a harder question: if a capable adversary set out to hurt this business, would anyone notice in time? Veiliux red team engagements are objective-driven. We agree the crown jewels up front, whether that is customer data, payment flows, domain admin or a trade-secret repository, and then pursue them the way a real actor would, across technical, human and physical vectors.
Scenarios are threat-led rather than generic. We profile the groups that actually target your sector, emulate their tooling and techniques mapped to MITRE ATT&CK, and operate with the same patience they do: low-and-slow reconnaissance, living-off-the-land tradecraft, and deliberate attempts to stay under your alerting thresholds. Phishing, pretexting and physical intrusion are included where the rules of engagement allow, because real attackers do not respect scope boundaries.
The value of a red team is measured by what your defence learns. Every engagement closes with a purple team debrief where our operators replay each successful step alongside your SOC, confirm whether it was detected, and tune the detection logic until it fires reliably. You receive an attack narrative, a detection gap report and a prioritised hardening plan, plus a re-run of selected techniques to prove the new detections work.
How is red teaming different from a penetration test?
A penetration test maximises vulnerability coverage within a defined scope. A red team maximises realism, pursuing a business objective by any agreed vector while measuring whether your people and tooling detect and respond.
Who knows the test is happening?
Only a small white cell you nominate. Wider knowledge dilutes the measurement of your detection and response capability.
Threat intelligence turns noise into decisions: who is targeting you, how they operate and what to do about it this week.
Most organisations already receive more security data than they can read. The gap is not information but interpretation: which of the thousands of daily indicators actually matters to your estate, your sector and your exposure right now. Veiliux threat intelligence services close that gap by combining automated collection with analyst judgement, so every alert that reaches your team is relevant, contextualised and actionable.
Collection spans the open, deep and dark web: criminal forums, ransomware leak sites, Telegram channels, paste sites, code repositories and credential markets. We watch for your brand, domains, executive identities, leaked credentials, exposed secrets and mentions of your suppliers. When a new campaign targets your sector or a zero-day touches your stack, you hear it from us with a clear assessment of whether and how it applies to you.
Delivery is built for action rather than reading. Tactical outputs are machine-consumable IOC and TTP feeds that integrate directly with your SIEM, EDR and firewall tooling. Operational outputs map actor tradecraft to MITRE ATT&CK so your SOC can hunt proactively. Strategic outputs give leadership a quarterly view of the threat landscape, your exposure trend and the investments that would change it.
Can feeds integrate with our existing tools?
Yes. Indicators are delivered in STIX/TAXII and plain feed formats compatible with major SIEM, EDR and firewall platforms.
Do you monitor for leaked credentials?
Yes. Credential dumps, stealer-log marketplaces and combo lists are monitored continuously for your domains and executive identities.
A source code audit reads the application the way its author never did, hunting logic flaws, auth bypasses and data exposure that tools cannot see.
Automated scanners are good at pattern-matching known bug classes and poor at everything that makes an application yours: business logic, authorisation flows, race conditions, cryptographic misuse and the assumptions developers made at 2am. A Veiliux source code audit puts experienced reviewers inside your codebase to find exactly those flaws, before someone less friendly does.
The review is manual first and tool-assisted second. We trace the flows attackers care about, authentication and session management, authorisation decisions, payment and financial logic, file handling, deserialisation, cryptography and secret management, reading code line by line and building the abuse cases as we go. SAST, dependency and secret scanning widen coverage across the full repository, and every machine-generated finding is verified by hand so your developers never receive a false-positive dump.
Findings are delivered as a developer would want them: the exact file and line, a working proof of concept or exploitation narrative, the business impact, and a concrete remediation suggestion that fits your framework and conventions. We review in your own tooling where possible, comment directly on pull requests when invited, and re-audit the fixes so you can demonstrate closure to customers and auditors.
Which languages do you cover?
JavaScript, TypeScript, Python, Java, C#, Go, PHP, Ruby, C and C++ are covered routinely, with other stacks available on request.
How is access to our code handled?
Under NDA, through read-only access to your repositories or an archived snapshot, with all material purged at the end of the engagement.
AI systems fail in ways classical scanners never look for: manipulated prompts, poisoned data and leaked model context.
AI systems introduce a failure surface that traditional scanners are blind to. The model is not just code; it is code, weights, prompts, retrieval data, tool permissions and the humans who trust its output. Veiliux tests all of it. Adversarial prompt work covers direct and indirect injection, jailbreak chains, system-prompt extraction, unsafe tool invocation and agent loops that can be steered into destructive actions on your infrastructure.
Data handling receives equal attention. We trace what enters training sets, embeddings and retrieval stores, then test whether regulated or customer-segregated data can be recalled by the wrong tenant. Multi-tenant RAG deployments are a frequent source of silent leakage: retrieval filters that work in the happy path frequently fail under crafted queries, encoded payloads or language switching.
The engagement closes with guardrail validation and a supply-chain review. We measure whether output filtering, rate limits, refusal behaviour and human approval steps actually hold under sustained pressure, and we assess model provenance, third-party inference providers, plugin ecosystems and the blast radius of a compromised dependency. Findings map to the OWASP Top 10 for LLM Applications and to NIST's AI Risk Management Framework so they slot straight into an existing governance programme.
Do you test open-source and hosted models?
Yes. Self-hosted, API-hosted and fine-tuned models are all in scope, along with the orchestration layer around them.
Smart contract defects are permanent once deployed, so the review happens before mainnet and after every material change.
Smart contract defects are permanent in a way ordinary software bugs are not: once deployed, the flawed logic is immutable and the funds it guards are liquid. Veiliux reviews contracts before mainnet and after every material change, combining line-by-line manual review with symbolic execution and property-based fuzzing to find reentrancy, access-control gaps, arithmetic errors, unchecked external calls and oracle manipulation.
Economics are reviewed alongside code. Many exploited protocols contained no coding error at all, the incentives allowed an attacker to profit through legitimate transactions, often amplified by flash loans or governance capture. We model those scenarios explicitly, including price-feed dependency, slippage, liquidation logic and voting thresholds.
Scope extends past the contracts themselves to deployment scripts, upgrade proxies, admin key custody, multisig thresholds and off-chain components such as relayers and indexers. After remediation we run a verification pass and, if you need one for your community or exchange listing, produce a public-ready summary of the audit and its outcome.
Compliance work is framed around evidence: what an auditor will ask for, and where that artefact comes from in your environment.
Compliance projects stall when they are run as documentation exercises. Veiliux frames the work around evidence: for every control, we identify what an auditor will ask for, which system produces that artefact and who owns it. That turns an abstract framework into a finite list of engineering and process tasks with named owners and dates.
We support ISO 27001, SOC 2 Type I and II, PCI DSS, HIPAA, GDPR and regional regulations across the UK, US, UAE and Saudi Arabia. Where you pursue several at once, controls are mapped to a single internal baseline so one piece of evidence satisfies multiple frameworks instead of being rebuilt per audit.
Policies and procedures are written to describe how your teams already work, with the minimum change necessary to be compliant, policies that contradict daily practice fail on their first audit sample. We stay engaged through the audit itself, answering auditor queries, preparing sample sets and closing observations before they become non-conformities.
How quickly can we be audit-ready?
A focused ISO 27001 or SOC 2 readiness programme typically runs three to six months, driven mainly by the evidence period an auditor requires.
Forensic work preserves evidence first and answers questions second, so the findings hold up internally and in court.
Forensic engagements preserve evidence first and answer questions second. Acquisition is performed under documented chain of custody across disks, memory, cloud tenants, endpoints, mobile devices and log platforms, with hashes recorded at every step so the material remains admissible if the matter escalates to litigation or regulatory action.
Analysis reconstructs a defensible timeline: how the actor obtained initial access, how long they were resident, what they touched, which credentials they used, what was staged for exfiltration and whether data actually left the estate. That last question is usually the one determining your notification obligations, and it deserves an evidence-backed answer rather than an assumption.
Beyond intrusions, the same discipline supports insider misuse, fraud, intellectual property theft and employment disputes. Findings are delivered in a written report suitable for regulators, insurers, boards and legal counsel, and our examiners can provide statements or expert testimony where required.
When an incident is live the priority order is contain, evict, recover, then learn, with clear communication throughout.
During a live incident the order of operations is fixed: contain, evict, recover, learn. Veiliux responders join within the agreed response window, establish a single source of truth for the timeline, and work alongside your team rather than displacing it. Early triage confirms scope, affected systems, the actor's likely objective and whether regulated data has been touched.
Containment balances speed against evidence. Isolating a host is trivial; isolating it without destroying volatile memory, tipping off the attacker or breaking a business-critical process requires judgement. We sequence credential rotation, token revocation, session invalidation and network segmentation so eviction happens once rather than repeatedly.
Recovery support covers clean rebuilds, restoration validation, integrity checks and heightened monitoring for re-entry attempts, which are common in the fortnight after eviction. The engagement finishes with a post-incident review: root cause, control failures, detection gaps and a prioritised hardening plan, plus assistance with regulator, insurer and customer communication where needed.
Can you help if we are under attack right now?
Yes. Request a quote or contact us directly and mark it urgent; retainer clients receive a contractual response time.
Hardening turns default installations into defensible baselines and keeps them that way.
Default installations are built for compatibility, not for defence. Hardening converts them into baselines that resist common attack techniques while remaining operable. Veiliux works from CIS Benchmarks and vendor guidance, then adapts each control to your environment so nothing breaks in production.
Coverage spans Windows and Linux servers, endpoints, Active Directory and identity providers, cloud accounts across AWS, Azure and GCP, containers and Kubernetes, and network devices. Particular attention goes to the controls attackers care about: administrative tiering, credential caching, legacy protocols, logging fidelity, service accounts and lateral-movement paths.
Hardening only holds if drift is measured. We deliver baselines as code where possible, wire compliance checks into your existing pipelines and provide a scorecard so leadership can see the risk reduction over time rather than accepting a one-off improvement that quietly erodes.
Resilience is proven by rehearsal, not by documentation.
Cyber resilience is the assumption that prevention will eventually fail and the business must keep operating anyway. Veiliux assesses that assumption against evidence: recovery time and recovery point objectives are not credible until they have been tested against a realistic destructive scenario.
We review backup architecture for immutability, isolation and credential separation, the properties ransomware operators specifically attack, then run restoration tests on representative systems to measure the true recovery time rather than the documented one. Dependencies are mapped so that restoring a system does not stall waiting for a service nobody listed.
Tabletop exercises put decision-makers under the same pressure, covering ransom decisions, regulatory notification, customer communication and the point at which you invoke third parties. The output is a resilience scorecard with prioritised gaps, so continuity investment goes where the recovery actually breaks.
Defence in depth means no single control failure becomes a breach.
Defence in depth fails when it becomes tool accumulation. Veiliux consulting starts by mapping controls to the attack paths that matter for your business, exposing where you have four overlapping products covering one stage and nothing covering another.
From that map we build a zero-trust roadmap: identity as the primary perimeter, device posture as a condition of access, segmentation that assumes breach, and telemetry sufficient to detect movement between zones. Each phase is scoped against budget and operational capacity, because a roadmap the team cannot deliver is a document, not a strategy.
We remain vendor-neutral. Where an existing product can be tuned to close a gap, that is the recommendation; where consolidation reduces both cost and complexity, we say so and quantify it. The deliverable is a phased plan with owners, dependencies, expected risk reduction and the metrics that will demonstrate it.
Data stolen today can be decrypted after quantum computers mature, which makes cryptographic inventory urgent now.
Harvest-now-decrypt-later is already an operational risk: encrypted traffic and archives captured today can be decrypted once cryptographically relevant quantum computers exist. Any data with a confidentiality lifetime measured in years, health records, financial contracts, state and defence material, intellectual property, is exposed to that timeline now.
The first deliverable is a cryptographic inventory. Most organisations cannot answer which algorithms, key sizes, certificates and libraries are in use across applications, appliances, embedded devices and third-party services. We build that inventory, flag deprecated primitives and rank each asset by data lifetime and migration difficulty.
Migration planning then targets the NIST post-quantum standards, ML-KEM for key establishment and ML-DSA or SLH-DSA for signatures, with hybrid deployments during transition. We also address crypto-agility itself, so the next algorithm change is a configuration exercise rather than another multi-year programme.
Permissioned ledgers move trust into infrastructure, so the infrastructure has to be designed for adversaries.
Permissioned ledgers solve trust between organisations, but they inherit every operational security concern of a distributed system plus a few of their own. Veiliux threat-models the network design first: membership and identity issuance, endorsement policies, consensus configuration, channel or subnet segregation and what a malicious participant could achieve.
Key management usually determines the security of the whole deployment. We design custody for signing keys, HSM integration, rotation and revocation, and recovery procedures that do not depend on a single administrator, then verify the design holds against realistic insider scenarios.
Deployment work covers node hardening, secure smart contract or chaincode review, API and gateway exposure, monitoring for ledger-level anomalies, and the operational runbooks the platform team needs to run it safely after handover.
Programme detail for every Veiliux training track, including who it suits, what is covered and how progress is measured.
Most breaches still start with a person, so awareness training is measured on behaviour change rather than attendance.
Awareness training changes behaviour only when it is measured and specific. Veiliux runs a baseline phishing simulation before any content is delivered, so improvement is demonstrable rather than assumed. Campaigns use realistic pretexts drawn from current attacker tradecraft, payroll changes, supplier bank detail updates, MFA fatigue prompts and QR-code lures, tailored to your sector and brand.
Modules are role-based. Finance staff are drilled on invoice fraud and payment verification, executives and their assistants on impersonation and travel-period targeting, developers on credential handling and repository hygiene, and frontline staff on physical tailgating and device loss. Sessions are short, scenario-driven and delivered in language people actually use.
Reporting gives leadership click rate, report rate and time-to-report by department, tracked across campaigns. The reporting metric matters most: an organisation where staff raise the alarm in two minutes survives incidents that sink one where nobody speaks up.
Engineering teams learn hardening by doing it in a lab that mirrors their production stack.
Infrastructure security training is delivered in labs, not slides. Engineers work in a dedicated environment where they harden real systems, break them, and observe the telemetry their changes produce, the fastest way to convert a benchmark document into working knowledge.
Content covers Linux and Windows hardening, Active Directory tiering and delegation, network segmentation, secure remote access, cloud identity and workload configuration, container and Kubernetes security, patch and vulnerability workflow, and logging that supports investigation rather than just storage.
Each module pairs an attack with the corresponding defence, so participants see why the control exists. Courses can be aligned to certification tracks where teams need formal recognition, and the lab remains available after delivery for continued practice.
Designed for critical national infrastructure and public-sector teams facing state-aligned adversaries.
Critical national infrastructure faces adversaries with different objectives from criminal groups: disruption, positioning and influence rather than immediate financial return. This programme teaches teams to recognise that tradecraft and respond proportionately.
Material is built on documented campaigns against energy, transport, telecom, water and government sectors, walking through initial access, persistence in OT and IT environments, living-off-the-land techniques and the indicators that distinguish state-aligned activity from commodity crime.
Delivery includes response drills and intelligence-handling practice: classification discipline, sharing with national bodies and sector CERTs, and the escalation decisions that must be made quickly and cannot be improvised. Content and delivery are adapted to the clearance and handling requirements of the organisation.
Secure coding training built around your own repositories rather than generic examples.
Developer security training works when it uses the team's own code. Veiliux builds the course around your languages, frameworks and repositories, so every example is recognisable and every fix is immediately applicable.
Labs cover the OWASP Top 10 in practice, injection, broken access control, authentication and session flaws, SSRF, insecure deserialisation, and the API-specific issues that dominate modern breaches, alongside secrets management, dependency and supply-chain risk, and secure design review.
The DevSecOps track integrates SAST, DAST, dependency and IaC scanning into your pipeline with thresholds that block genuinely dangerous changes without drowning teams in noise. Developer scorecards track defect classes over time so security becomes a measurable engineering quality metric.
For internal audit and security teams that must evidence control coverage independently.
Internal audit and assurance teams are frequently asked to prove control coverage without having been taught how. This course gives them a repeatable methodology: scoping against a control framework, sampling, evidence collection, testing technique and defensible conclusions.
Practical sessions cover network discovery and topology validation, firewall and ACL review, segmentation verification, privileged access checks, configuration baselines and log coverage assessment, using tooling participants can continue to run afterwards.
A substantial part of the programme is report writing. Auditors learn to state findings with evidence, rate them consistently, avoid unsupported assertions and write recommendations that engineering teams can act on, the difference between an audit that improves security and one that generates a filing.
Sector-specific detail on the threats we see, the regulations that apply and how engagements are adapted.
Financial institutions face targeted fraud, payment abuse and strict regulatory scrutiny at the same time.
Banks, fintechs and payment platforms are tested against the flows that carry money and the controls regulators examine. Veiliux scopes engagements around payment initiation and authorisation, card data environments, open banking APIs, treasury and settlement systems, customer onboarding and the fraud controls layered across them.
Testing looks for logic abuse as much as technical vulnerability: transaction replay, race conditions on balance updates, limit bypass, currency and rounding manipulation, and account takeover chains through weak recovery flows. These issues rarely appear in automated scans and are exactly what organised fraud groups pursue.
Reporting is prepared for regulator and board consumption, mapped to PCI DSS, DORA, PSD2, SAMA and other applicable regimes, with the evidence pack that supervisors and acquiring banks expect to see attached.
Carrier environments combine legacy signalling with modern cloud cores and enormous subscriber datasets.
Carrier environments combine IT, core network and OSS/BSS estates at a scale most testing methodologies were not designed for. Veiliux engagements are scoped to that reality: subscriber data stores, provisioning and billing chains, roaming and interconnect interfaces, signalling exposure and the management planes that sit above them.
Subscriber data is the primary asset and the primary regulatory risk. We trace where it is replicated across CRM, analytics, partner integrations and backups, then test whether access controls hold across each copy rather than only at the front door.
Work is planned around change freezes and service availability, using passive techniques on live network elements and lab replication for anything intrusive, so assurance is obtained without risking subscriber-affecting outages.
Patient safety and patient privacy are the same problem once clinical systems are networked.
Healthcare providers must protect patient data across a technology estate they only partly control: EHR platforms, imaging systems, laboratory interfaces, patient portals, clinical devices and a long tail of vendor-managed equipment that cannot be patched on your schedule.
Veiliux prioritises PHI exposure paths, interface engines, HL7 and FHIR endpoints, shared clinical workstations, unsegmented device VLANs and third-party integrations, because that is where breach volume concentrates. Medical device testing is performed with clinical safety oversight and never against equipment in patient use.
Deliverables are structured as HIPAA evidence: risk analysis input, control-by-control findings, remediation guidance and documentation your privacy officer can file directly. Where a device cannot be remediated, we specify the compensating controls that make the residual risk defensible.
In OT environments an intrusive scan can be more damaging than the attacker, so method matters.
In oil and gas, safety and availability outrank confidentiality, and any assessment that ignores that is unusable. Veiliux uses passive discovery, traffic analysis and configuration review across OT environments, reserving active testing for maintenance windows or offline replicas agreed in advance with the process safety team.
The core question is almost always segmentation: whether an intruder in the corporate network can reach the process network through jump hosts, vendor remote access, historians, shared credentials or engineering laptops that move between zones. We test those crossings specifically and document them as paths, not as isolated findings.
Recommendations respect the operational reality that control systems have decade-long lifecycles and cannot always be patched. Where upgrade is impossible, we specify segmentation, monitoring and access controls that reduce exposure without touching the process itself, mapped to IEC 62443.
Defence programmes require security depth and disciplined handling of sensitive material.
Aerospace and defence programmes carry security obligations that extend to every supplier and every piece of data in transit between them. Veiliux engagements begin with data handling: classification, storage jurisdiction, personnel requirements and the controls governing what leaves the programme boundary.
Assessment covers mission and ground systems, engineering environments, manufacturing operational technology and the supply chain, the route through which the most damaging compromises in this sector have historically occurred. Supplier assessment includes both technical exposure and the contractual assurance behind it.
Reporting is prepared to the handling standard your programme requires, and our testers work under the vetting and nationality constraints stipulated by the contract. Findings map to the frameworks your authority recognises, including NIST SP 800-171 and equivalent national schemes.
How our managed solutions are built, staffed and measured once they are running in your environment.
The Cyber Emergency Response Centre exists to shorten the distance between detection and containment.
The Cyber Emergency Response Centre exists to remove the delay between detecting an incident and containing it. Under retainer, named responders are contractually committed to a response time, already hold the context of your environment and can begin work without a procurement cycle, the single largest avoidable cost in most incidents.
Onboarding builds the material response depends on: asset and identity inventory, network and cloud architecture, escalation contacts, legal and insurer notification requirements, and pre-approved containment authority so a responder can isolate a host at three in the morning without waiting for a committee.
Playbooks are pre-built for ransomware, business email compromise, data theft, destructive attacks and insider incidents, and rehearsed with your team before they are needed. During an incident CERC coordinates the parties that otherwise consume executive attention, law enforcement, regulators, insurers, external counsel and communications, while technical containment proceeds in parallel.
After the event, a structured review feeds detection and hardening improvements back into your environment. Retainer hours not consumed by incidents are used for that work, so the arrangement produces value in quiet quarters as well as bad ones.
What response times are available?
Retainers are offered with one-hour, four-hour and next-business-day response tiers, selected per client and written into the agreement.
A SOC is only useful if the alerts reaching analysts are worth their attention.
A security operations centre is only worth its cost if the alerts reaching analysts deserve their attention. Veiliux builds the pipeline that makes that true: telemetry from endpoint, network, identity, cloud and SaaS is normalised, enriched with asset and user context, and correlated by AI models that suppress the recurring noise which consumes most in-house SOC capacity.
Human analysts operate 24/7 across three shifts, triaging what survives correlation, investigating with full access to the enriched timeline, and executing agreed response actions, host isolation, session revocation, credential disablement, within pre-authorised limits. Anything outside those limits escalates to your named contacts with a recommendation, not a question.
Detection engineering runs as a continuous programme rather than a deployment. Coverage is mapped to MITRE ATT&CK, gaps are prioritised against threats relevant to your sector, new detections are tested before promotion and noisy rules are retired every sprint. You receive the content, not just the service.
Monthly reporting covers alert volume and disposition, mean time to detect and respond, coverage changes, notable investigations and the hardening actions that would remove whole alert categories. The intent is a SOC that measurably shrinks your attack surface over time rather than one that simply forwards alerts.
Can the SOC use our existing SIEM?
Yes. We operate on your platform where one exists, or provide the pipeline if you prefer not to run it in house.
What each deployment involves, from design and pilot through rollout, tuning and handover.
Endpoint tooling only pays off after policy tuning and response automation are in place.
EDR and XDR platforms deliver value after tuning, not after installation. Veiliux runs selection against your actual threat profile and operating systems, pilots the shortlist on representative endpoints and measures detection quality and performance impact before any fleet-wide commitment.
Rollout is phased across Windows, macOS, Linux and mobile estates, with exclusions reviewed rather than inherited, copied exclusion lists are a routine cause of blind spots. Policy tuning removes noise while preserving coverage, and detection gaps found during pilot are closed with custom rules.
Automation is configured last and deliberately: isolation, process termination and rollback workflows with guardrails that prevent an automated action from taking out a production system. Handover includes runbooks, an escalation model and training for the team that will operate the platform.
A SIEM succeeds or fails on log quality, use-case content and analyst workflow.
SIEM programmes fail on three things: log quality, use-case content and analyst workflow. Veiliux addresses them in that order. Log sources are prioritised by the attack coverage they provide rather than by what is easiest to onboard, and parsing and normalisation are validated field by field so detections do not silently break.
Detection content is built as a library mapped to MITRE ATT&CK, with each rule documented for intent, data dependency, expected volume and response action. Rules enter production only after tuning against your baseline, and the library is reviewed on a cycle so coverage tracks changes in the estate.
Retention and cost design is treated as an engineering problem: hot, warm and archive tiers sized against investigation reality and regulatory obligation. Dashboards and runbooks are handed to your analysts with training, so the platform remains operable and extensible without us.
Most firewall estates carry years of accumulated rules nobody is willing to remove.
Most firewall estates carry a decade of accumulated rules nobody is willing to remove. Veiliux begins with a rule-base audit: shadowed, redundant, expired and overly permissive rules are identified with usage evidence, so removals are made on data rather than nerve.
Design work covers next-generation firewall deployment in high availability, macro and micro-segmentation aligned to real application dependencies, inspection strategy for encrypted traffic, and policy structure that stays legible as it grows.
The final phase is governance. Change process, naming standards, rule expiry, periodic recertification and documented ownership are put in place so that hygiene survives after the project ends, which is where most segmentation efforts quietly unwind.
Business-critical platforms need secure configuration as part of deployment, not after it.
Business-critical platforms are usually deployed for function first, with security retrofitted under time pressure. Veiliux integrates hardening into the deployment itself: installation baselines, environment separation, secrets management and network exposure defined before go-live rather than after the first audit.
Identity is designed rather than default. SSO and MFA are enforced across every access path, roles are built to least privilege from the business process rather than from vendor templates, and privileged administration is separated from routine use.
Integrations receive specific attention because they are where enterprise platforms leak: API exposure, service accounts, file transfer paths and reporting extracts are reviewed and constrained. Handover includes operational runbooks, patching ownership and a configuration baseline to test against later.
Data loss prevention fails when it blocks legitimate work, so tuning precedes enforcement.
Data loss prevention fails when it obstructs legitimate work, so Veiliux never begins with enforcement. The first phase is discovery and classification across endpoints, email, cloud storage and SaaS, producing an evidence-based picture of where regulated and sensitive data actually resides, usually in more places than expected.
Policies are then run in monitor mode long enough to understand normal business behaviour, with false positives tuned out before anything is blocked. Only high-confidence, high-impact scenarios move to enforcement first; broader coverage follows once trust in the tooling is established.
The deployment also delivers insider-risk visibility and an investigation workflow: who can review an alert, what evidence is retained, how HR and legal are engaged, and how privacy obligations toward employees are respected. Policies are mapped to GDPR, HIPAA and PCI DSS obligations so the control set is defensible at audit.
Phishing-resistant authentication is the single highest-return control most organisations can deploy.
Phishing-resistant authentication remains the highest-return control most organisations can deploy, and the gap between basic MFA and phishing-resistant MFA is now the difference between deterring and stopping credential attacks. Veiliux deploys FIDO2 security keys and platform passkeys as the primary factor, with a documented fallback that does not reintroduce the weakness.
Conditional and risk-based access policy is designed alongside the rollout: device posture, location, application sensitivity and session lifetime, calibrated so that low-risk access stays frictionless and sensitive operations require stronger assurance.
Legacy authentication shutdown is planned explicitly, since it is the usual bypass around any MFA deployment. Protocol usage is inventoried, remaining consumers migrated and the protocols disabled on a published schedule. An adoption programme with clear communications, self-service enrolment and helpdesk preparation keeps support load low through the transition.
Build your scope in two minutes. We send a detailed estimate and a proposed test plan to your inbox.